AI-Driven Cyber GRC Platform forGlobal Compliance, Risk,and Audit Readiness
Waaqi helps organizations manage cybersecurity governance, risk, compliance, audits, policies, evidence, and third-party risk across global standards and regional regulations.
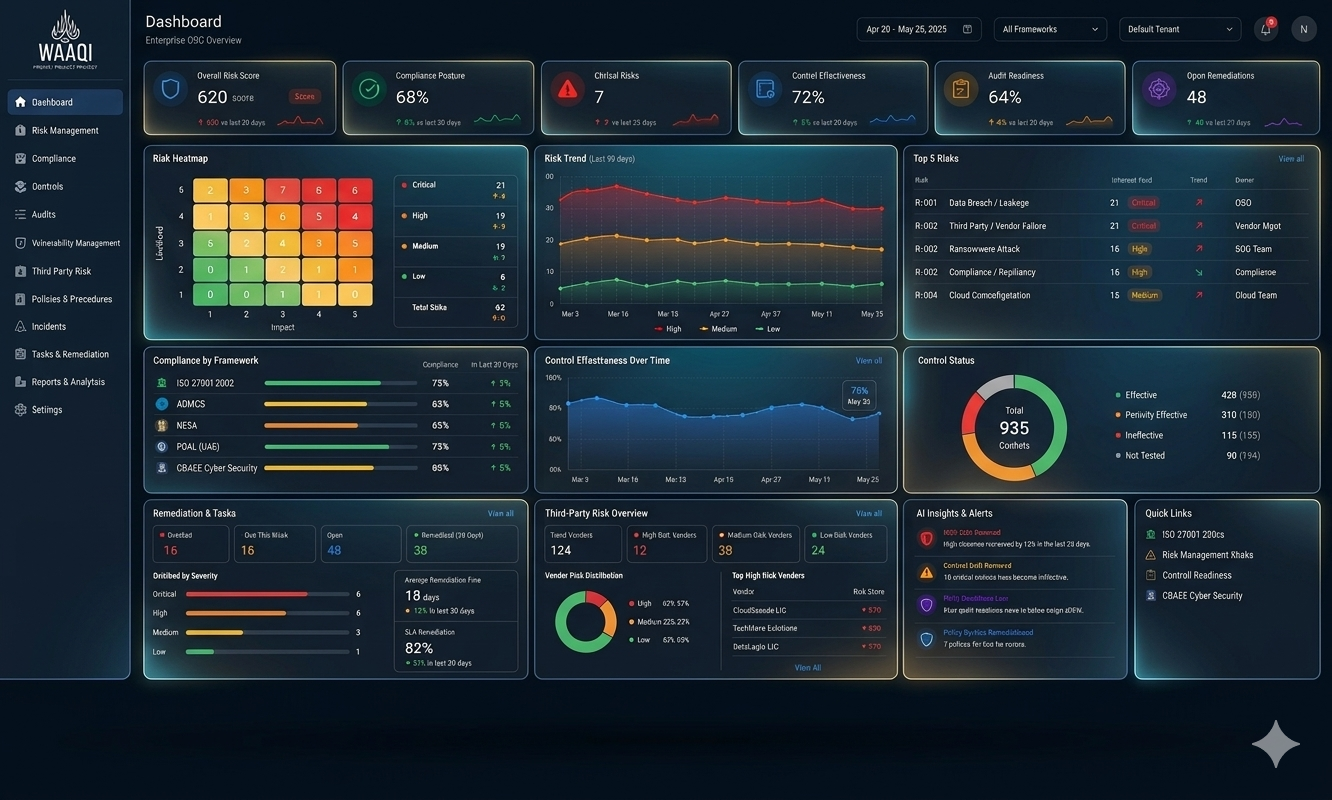
Every step deliberate.
Every record traceable.
No data is created automatically. No inherited configuration. Every policy, control, risk, and evidence record is gate-kept by user action ensuring records are intentional and defensible.
Gap Assessment
Framework-aligned scoring across every control Compliant, Partial, Gap, or N/A with prioritised recommendations and automated policy generation.
Statement of Applicability
Document control applicability, implementation status, and exclusion justifications with direct, auditable policy linkage.
Risk & Controls
Risk Register populated only on explicit user action. Deliberate records, intentional entries, defensible in any audit.
Operations & Monitoring
Asset discovery, vulnerability tracking, task management, security awareness, and TPRM all under one governed workspace.
Audit & Reporting
Centralise evidence, run control tests, capture findings, and export audit packs. Board-ready KPI and KRI dashboards on demand.
Built for every layer
of your compliance stack.
Tenant-Isolated Architecture
One pane of glass for
every control decision.
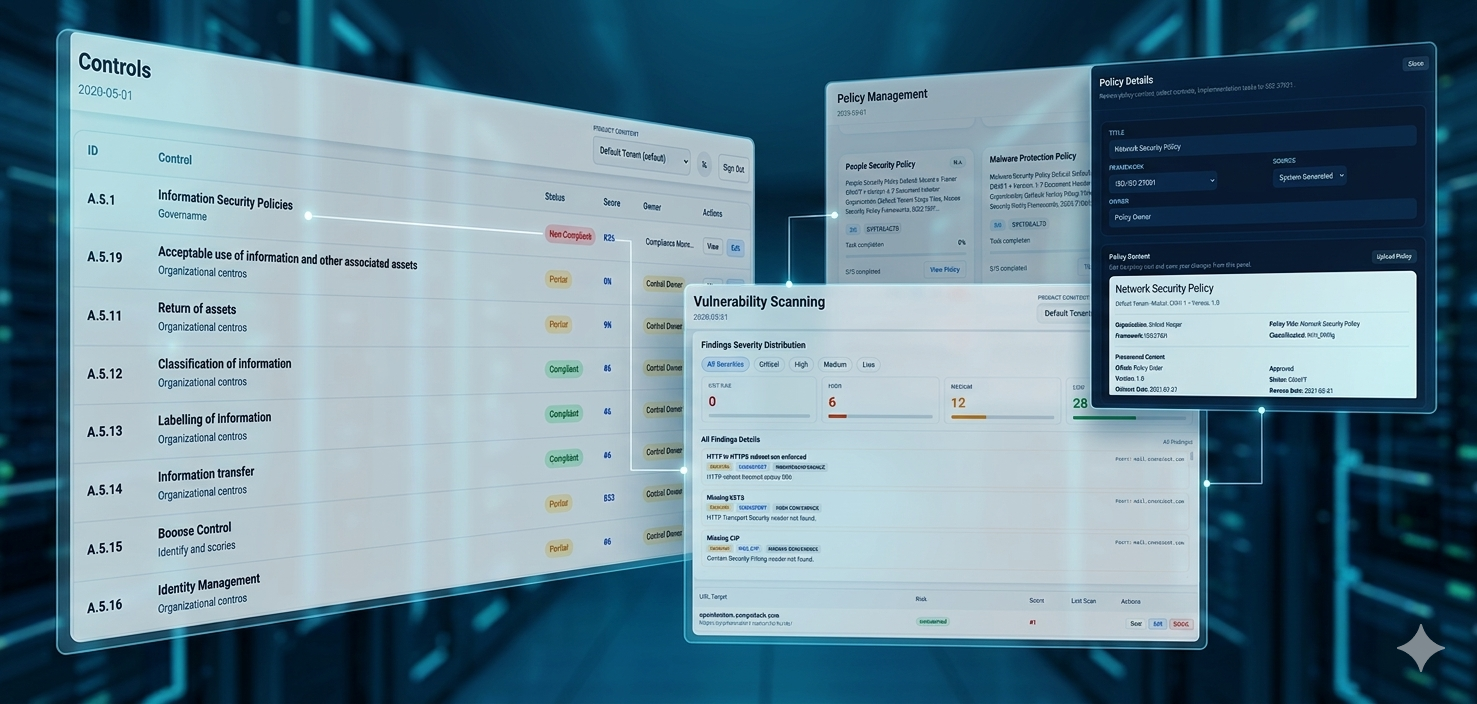
Inspect the full ISO 27001 Annex A control catalogue, drill into individual policy records, and triage live vulnerability findings all linked, scored, and audit-ready inside the same governed workspace.
- ▸Per-control compliance status, score, and owner
- ▸Policy library with version history and approvals
- ▸Severity-classified vulnerability triage queue
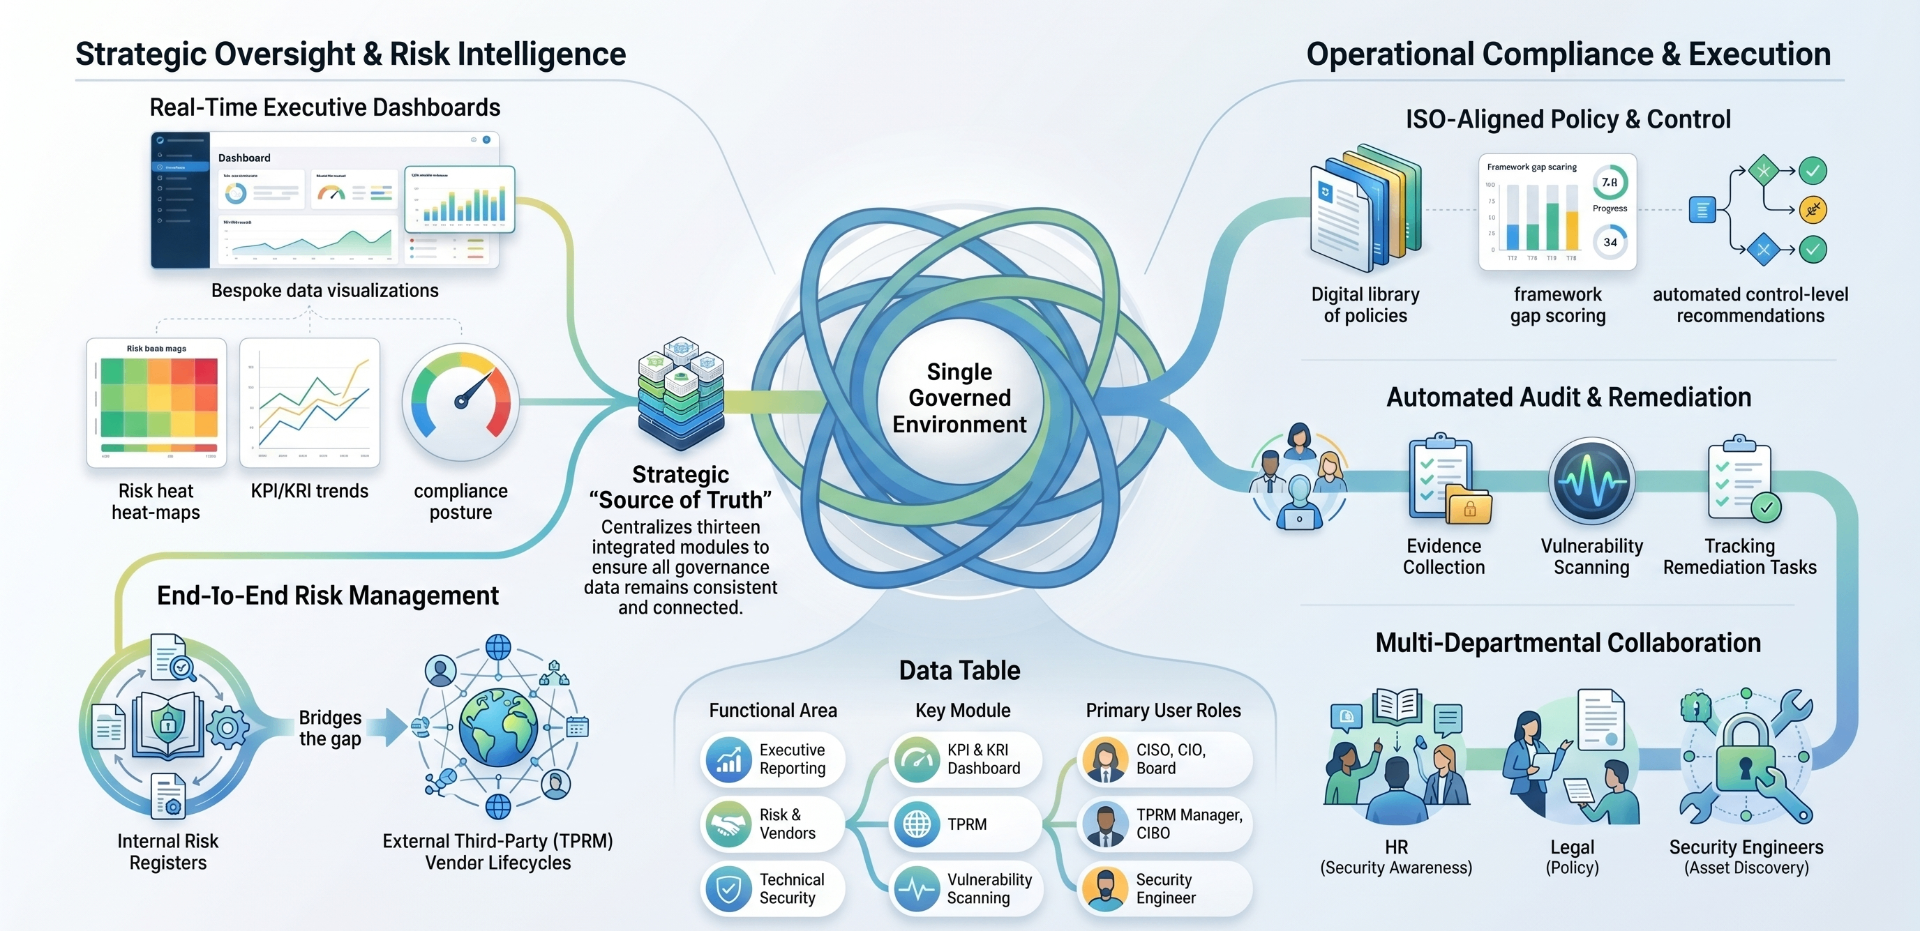
Everything in one governed workspace.
Thirteen integrated modules each purpose-built, all connected through a single source of truth.
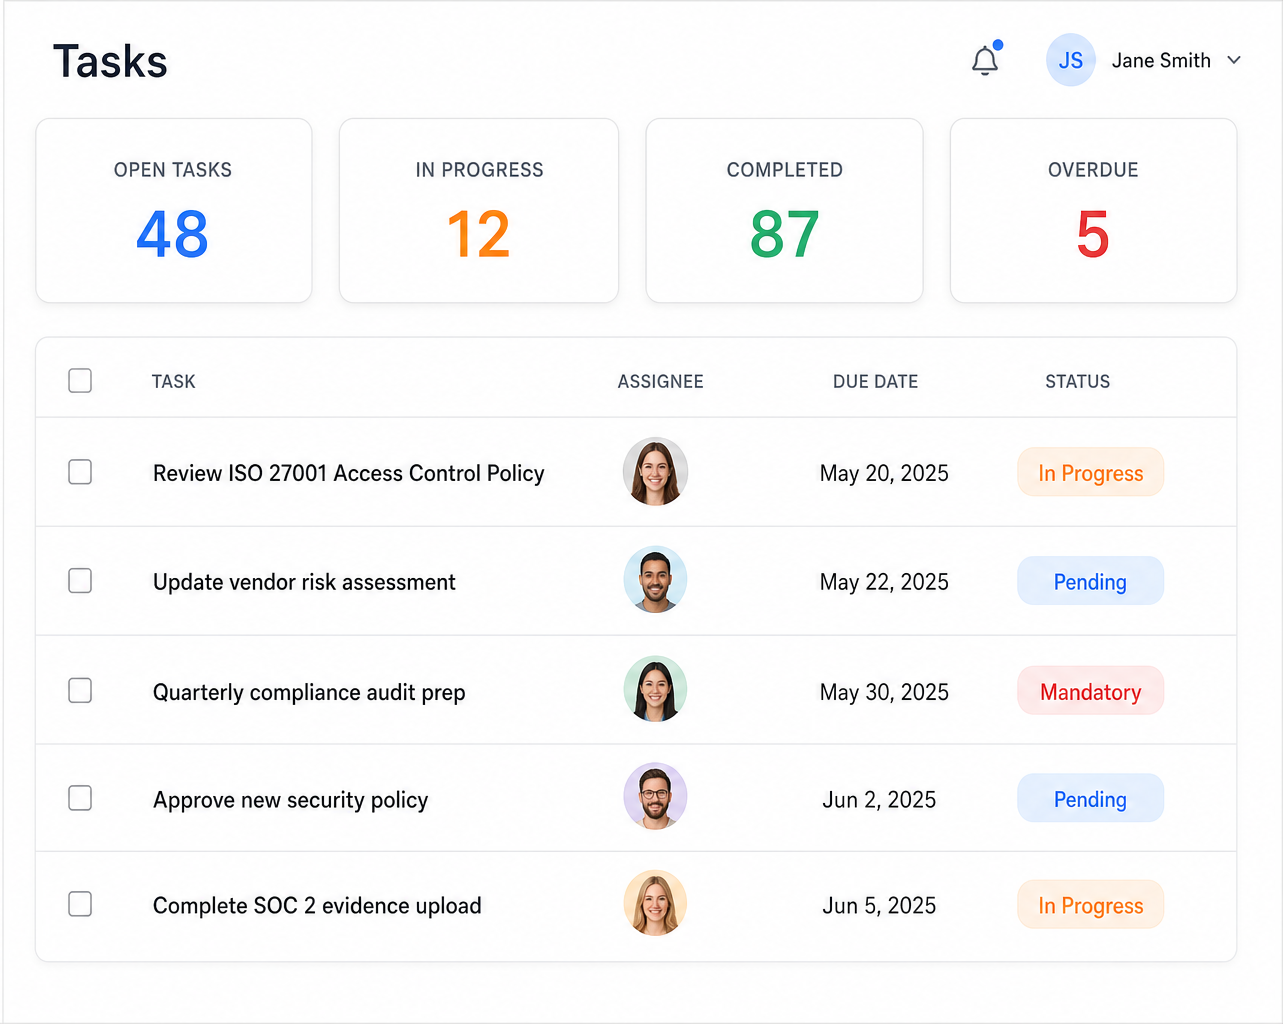
Operational control,
across every framework.
Track open remediation tasks, plan audit cycles, and measure security awareness coverage in a single executive view with every record traceable back to a control, policy, or finding.
- ▸Live task queue across all frameworks and owners
- ▸Quarter-based audit planning with approval gates
- ▸Awareness training completion and effectiveness scoring
Vendor risk.
Governed end-to-end.
A fully integrated TPRM module governing the complete vendor lifecycle from initial prospecting through structured offboarding with tier-based risk registers, assessment workflows, evidence tracking, and a comprehensive audit trail.
Vendor Lifecycle States
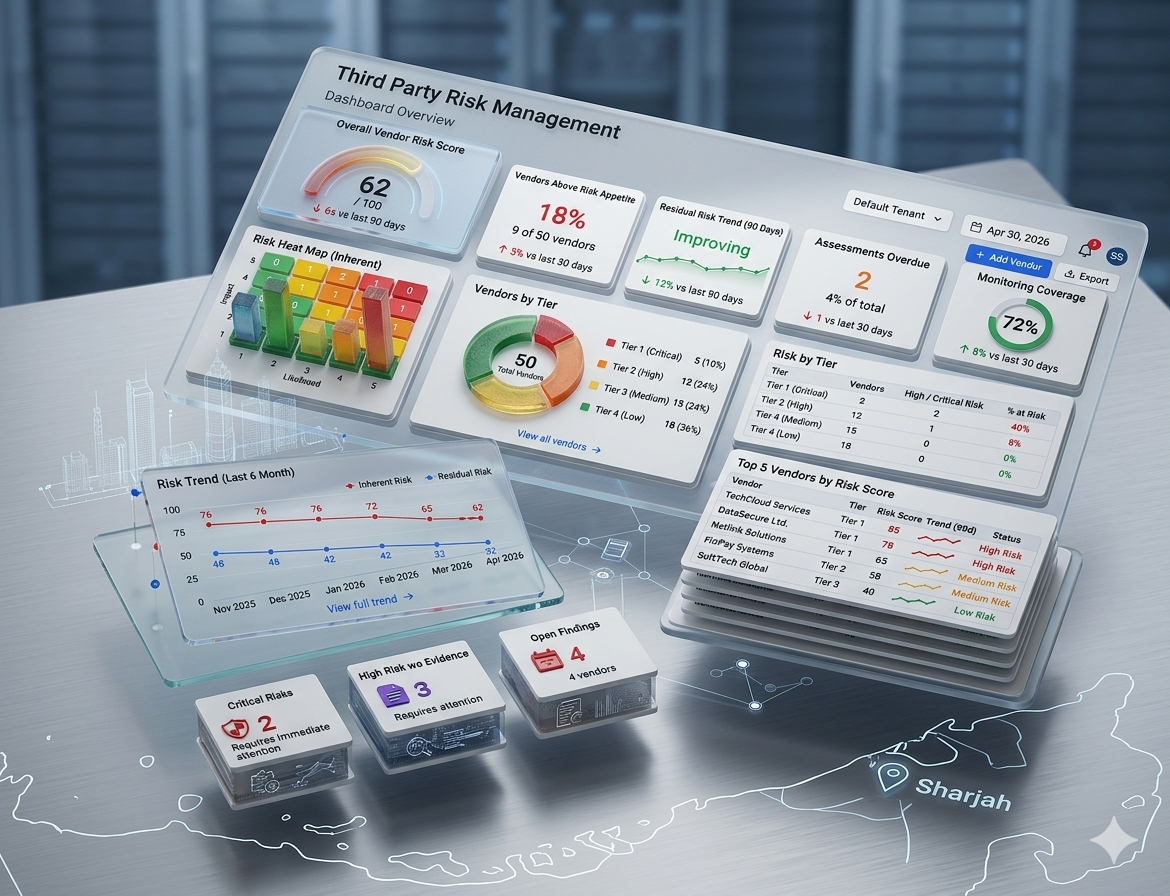
Vendor Lifecycle
Risk & Assessments
Evidence & Audit Trail
Built to enterprise standards.
Deployed where you need it.
Governance & Auditability
Security & Tenancy
Deployment Options
Built for global compliance.
Adaptable for local regulations.
Waaqi supports international cybersecurity and privacy frameworks while allowing organizations to manage region-specific regulatory obligations through configurable control mappings, evidence workflows, risk registers, and audit-ready reporting.
Global framework coverage
ISO 27001, SOC 2, NIST CSF, GDPR, PCI DSS, and HIPAA covered out of the box with up-to-date control catalogues.
Regional compliance support
UAE PDPL, KSA PDPL, ADHICS, SAMA CSF, and NCA ECC mapped to local regulator expectations and language.
Configurable control library
Tailor controls, ownership, and testing cadence to your sector, jurisdiction, and risk appetite without code.
Multi-framework mapping
Assess once, satisfy many. Reuse evidence and tests across overlapping global and regional frameworks.
Centralized evidence management
One governed repository for documents, attestations, and control tests linked to every framework requirement.
Executive risk visibility
Board-ready dashboards translating control posture, residual risk, and audit findings into clear executive insight.
Flexible deployment.
Sovereign data residency.
Waaqi can support different deployment models based on customer requirements, including cloud-hosted, region-hosted, and dedicated deployment options.
Cloud Deployment
Fully managed multi-tenant SaaS hosted on enterprise-grade cloud infrastructure with 24/7 monitoring, automated backups, and continuous updates.
Region-Specific Hosting
Region-specific hosting options that keep customer data within the jurisdiction of your choice to meet local regulatory and data sovereignty requirements.
Dedicated Tenant
A fully isolated single-tenant environment provisioned exclusively for your organization with dedicated compute, storage, and network boundaries.
Enterprise Deployment
On-premises or private cloud deployment within your own data centre or VPC, ideal for regulated entities with strict sovereignty mandates.
Built for regulated industries.
Designed for organisations across the GCC and beyond that require structured compliance governance with full audit traceability.
Banking & Financial Services
Central bank-regulated institutions requiring structured cyber-risk governance and audit-trail compliance.
Fintech & Payments
Licensing-driven firms building demonstrable compliance programmes for regulators and partners.
Telecommunications
Operators with critical national infrastructure obligations under sector-specific frameworks.
Government & Public Sector
Agencies requiring audit-ready governance with traceable evidence and policy accountability.
Healthcare & Pharma
Organisations handling sensitive health data under regional mandates such as ADHICS and PDPL.
Technology & SaaS
ISVs and IT service firms pursuing security certification readiness and enterprise customer trust.
Energy & Utilities
Critical infrastructure operators requiring risk-informed governance and operational resilience.
Insurance
Carriers managing multi-jurisdictional information security and regulatory obligations.
Quick value. Lasting impact.
Faster Assessment Cycles
Guided workflows eliminate ad-hoc spreadsheet-based gap analysis entirely.
Audit-Ready on Demand
Centralised evidence, SOA justifications, and control test records always available.
Cleaner Risk Register
Populated only through deliberate action reducing noise in board-level reporting.
Consistent Policy Posture
ISO-aligned structure reduces manual drafting overhead significantly across all teams.
Measurable Remediation
Task ownership and due-date tracking creates accountable, traceable closure rates.
Vendor Risk Under Control
TPRM lifecycle ensures no vendor is onboarded or offboarded without a documented trail.
Frequently asked questions
Everything you need to know about Waaqi's compliance, technical capabilities, and support.
Ready to govern your
compliance programme?
Schedule a live walkthrough or scoped pilot programme tailored to your organisation's framework and regulatory environment.
Deployment Regions